A trust score an AI agent can check before it connects
The AdminKit Agent Trust API is a planned endpoint an AI agent can call to get a trust score and supporting evidence, such as whether the endpoint requires authentication or matches known-bad patterns, before it connects to an unfamiliar MCP server or API, intended for agent framework maintainers and developers who need a documented reason for why a call proceeded or stopped.
Updated October 21, 2026
The problem
AI agents are increasingly built to discover and call tools and APIs they haven’t seen before, sometimes at runtime, based on what a task requires. That’s powerful, but it also means an agent can end up connecting to an endpoint with no prior knowledge of whether it’s trustworthy.
A human developer reviewing a new API integration usually does some due diligence first: checking certificates, reading documentation, looking at who operates it. An autonomous agent making that decision in milliseconds has no equivalent step unless one is built in.
Without some kind of check, an agent either has to blindly trust every endpoint it’s pointed at, or a developer has to hardcode an allowlist in advance, which defeats the point of letting the agent discover tools dynamically.
How it works
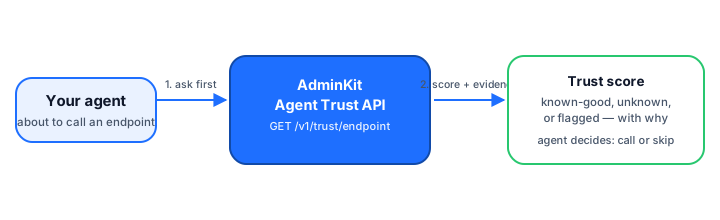
The plan is for an agent (or the code orchestrating it) to call the Agent Trust API with the endpoint it’s about to connect to, before making the real call. The API would return a score along with the evidence behind it — things like whether the endpoint requires authentication or matches known-bad patterns — and the agent or its developer decides whether to proceed, proceed with limits, or stop.
Who it’s for
- AI agent framework maintainers who want a built-in safety check before tool calls.
- Developers building autonomous agents that discover MCP servers or APIs dynamically.
- Teams that want a documented reason for why an agent proceeded or stopped, not just a black-box decision.
What exists today, what’s planned
| Capability | Status |
|---|---|
| Manually check an endpoint’s reachability and auth (mcp-check) | Free today |
| Manually check an endpoint’s TLS setup (ssl-check) | Free today |
| Trust API endpoint (GET /v1/trust/endpoint) | Early access |
| Scoring model | In development |
| Evidence citations returned with each score | In development |
A score reflects what AdminKit has observed about an endpoint at the time it was checked, not a continuous guarantee. Endpoints AdminKit hasn’t scanned simply won’t have a score yet, which is different from being marked unsafe.
Frequently asked questions
Is the Agent Trust API live?
No. It is early access / in development. Today there is no automated scoring; you'd need to manually check an endpoint with tools like mcp-check or ssl-check.
What does a trust score mean?
It's meant to be one input into a decision, built from evidence like whether the endpoint requires auth, how it's configured, and other signals AdminKit can observe. It is not a guarantee that an endpoint is safe.
Does a low score mean an endpoint is malicious?
Not necessarily. A low or missing score can simply mean AdminKit hasn't scanned that endpoint yet, or that the endpoint is missing common safeguards like authentication. It's not proof of malicious intent.
What will the API look like?
The plan is a simple call, for example GET /v1/trust/endpoint, that returns a score plus the evidence behind it, so a calling agent or its developer can decide how to proceed.
Does AdminKit vouch for endpoints with a high score?
No. AdminKit reports what it observed and scored; it does not vouch for or guarantee the behavior of any third-party endpoint, scanned or not.
Want early access to Agent Trust API: Score Endpoints Before Calling | AdminKit?
Tell us about your setup and we will reach out when it is ready for you — no spam, no newsletter.