A gateway that sits in front of your MCP server
The AdminKit MCP & Agent Gateway is a planned proxy that checks OAuth, enforces a tool allowlist, and logs every call before it reaches your MCP server, screening tool responses for obviously malicious content along the way so developers publishing an MCP server get authorization and an audit trail without building either one themselves.
Updated October 21, 2026
The problem
Model Context Protocol servers give AI agents the ability to call real tools: reading files, querying databases, hitting internal APIs. That’s useful, but it also means anyone who can reach the server, and anything the server is told to trust, inherits whatever access those tools provide.
Many MCP servers are stood up quickly during prototyping and never get a proper authorization layer added before they’re exposed. Even once auth is in place, there’s often no record of which tools were called, by whom, or what came back, which makes it hard to notice misuse or debug a problem after the fact.
Tool responses themselves are a second risk: if a tool returns content from an untrusted source, that content can contain instructions aimed at manipulating the agent reading it, a pattern commonly referred to as prompt injection.
How it works
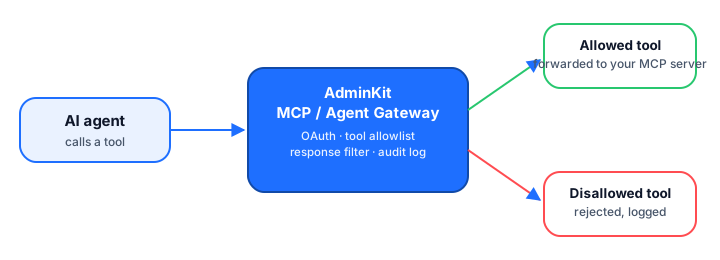
The plan is for the gateway to sit between the agent and your MCP server. Every call first goes through an OAuth check and a tool allowlist; calls that pass are forwarded to your server, and calls that don’t are rejected and written to an audit log. Tool responses coming back are also meant to be screened for obviously malicious content before reaching the agent.
Who it’s for
- Developers and startups publishing an MCP server who want authorization and logging without building it themselves.
- AI agency builders assembling agent workflows that call multiple third-party MCP servers.
- Teams that need an audit trail of what an agent actually did, not just what it was asked to do.
What exists today, what’s planned
| Capability | Status |
|---|---|
| Check if an MCP server is reachable and whether it requires auth (mcp-check) | Free today |
| Gateway proxy with OAuth enforcement | Early access |
| Per-tool allowlists | In development |
| Audit log of every call | In development |
| GitHub Action to scan MCP endpoints in CI | In development |
The gateway can only act on what passes through it. A server that’s also reachable directly, outside the gateway, still carries whatever risk existed before the gateway was added.
Frequently asked questions
Is the MCP Gateway available now?
No. It is early access / in development. Today you can check whether your MCP server is reachable and whether it requires auth with the free mcp-check tool.
What will the gateway actually see?
Only the traffic that passes through it. If a client bypasses the gateway and connects straight to your MCP server, the gateway has no visibility into that call.
Does the gateway replace authentication on my MCP server?
The plan is for the gateway to handle OAuth checks per the MCP authorization spec, so your server doesn't have to implement that itself. Your server can still run its own checks underneath it.
What does 'tool allowlist' mean here?
A list of which tools exposed by your MCP server are allowed to be called through the gateway. Calls to anything not on the list are rejected and logged instead of being forwarded.
Will it stop every prompt-injection attempt?
No single filter can guarantee that. The plan is for the gateway to screen obviously malicious content out of tool responses as one layer of defense, alongside the allowlist and audit log, not as a complete solution on its own.
Want early access to MCP & Agent Gateway for AI Tool Calls | AdminKit?
Tell us about your setup and we will reach out when it is ready for you — no spam, no newsletter.